AquilaX CSPM takes security from your repositories into the running cloud. It audits AWS, Azure, GCP and Kubernetes against CIS, NIST, PCI DSS, ISO 27001 and more, catches configuration drift, maps IAM privilege escalation paths and streams runtime threats as they happen.
Pre-deployment scanning leaves a gap. Once code is running in a cloud account, live settings drift from what the IaC says, identities collect extra permissions, and threats appear that no static scanner can see. CSPM watches all of it, continuously, in every cloud you use.
Unified inventory and compliance view across AWS, Azure, GCP, and Kubernetes. One dashboard replaces four separate security consoles and eliminates gaps between them.
Field-by-field comparison of your IaC definitions with the live cloud. Changes made by hand in the console, outside GitOps, get flagged straight away.
Maps privilege escalation paths, unused permissions, and over-permissioned roles that accumulated incrementally. Identifies the exact chain from compromised credential to sensitive data.
eBPF kernel events through Falco catch active threats like reverse shells, cryptomining and container escapes while they happen. None of these show up in a configuration audit.
Automated audit against CIS Benchmarks, NIST 800-53, PCI DSS 4.0, ISO 27001, SOC 2, HIPAA, DORA, NIS2, and GDPR. Export audit-ready evidence for any control on demand.
Policy-driven, opt-in remediation across AWS, Azure, and GCP. Every action is fully audited with context and exportable to your SIEM. Securitron AI suggests fixes before you enable automation.
AquilaX CSPM links each live cloud finding back to the IaC that created it, so you see which Terraform module or CloudFormation template made the misconfigured resource, along with its permissions and any runtime events.
AquilaX CSPM merges findings from six security engines into one resource graph, removes duplicates across sources and runs Securitron's false-positive filtering before anything reaches your dashboard.
Cloud configuration auditing across AWS, Azure, and GCP. Maps resources against CIS Benchmarks, NIST 800-53, PCI DSS, ISO 27001, SOC 2, HIPAA, DORA, and NIS2 with pass/fail per control.
SQL queries over cloud APIs for a full asset inventory and drift checks. Compares live resource settings with the IaC baseline field by field and catches every manual console change.
Deep AWS IAM policy analysis. Identifies resource exposure, privilege escalation paths, data exfiltration risks, and credential exposure from over-permissioned IAM policies and unused roles.
eBPF runtime detection at the kernel level. Catches reverse shells, cryptomining, container escapes and suspicious processes that no static scanner can see, and streams the events live.
Kubernetes posture assessment against NSA/CISA hardening standards with full MITRE ATT&CK mapping. Covers RBAC misconfigurations, insecure network policies, exposed secrets, and pod security violations.
Policy-based enforcement and auto-remediation across all three cloud providers. You define the action for each finding type (alert, tag, quarantine or delete), and every action is logged and exported to your SIEM.
The CSPM dashboard goes from executive compliance scores down to individual runtime events, inside the same AquilaX platform you already use for AppSec.
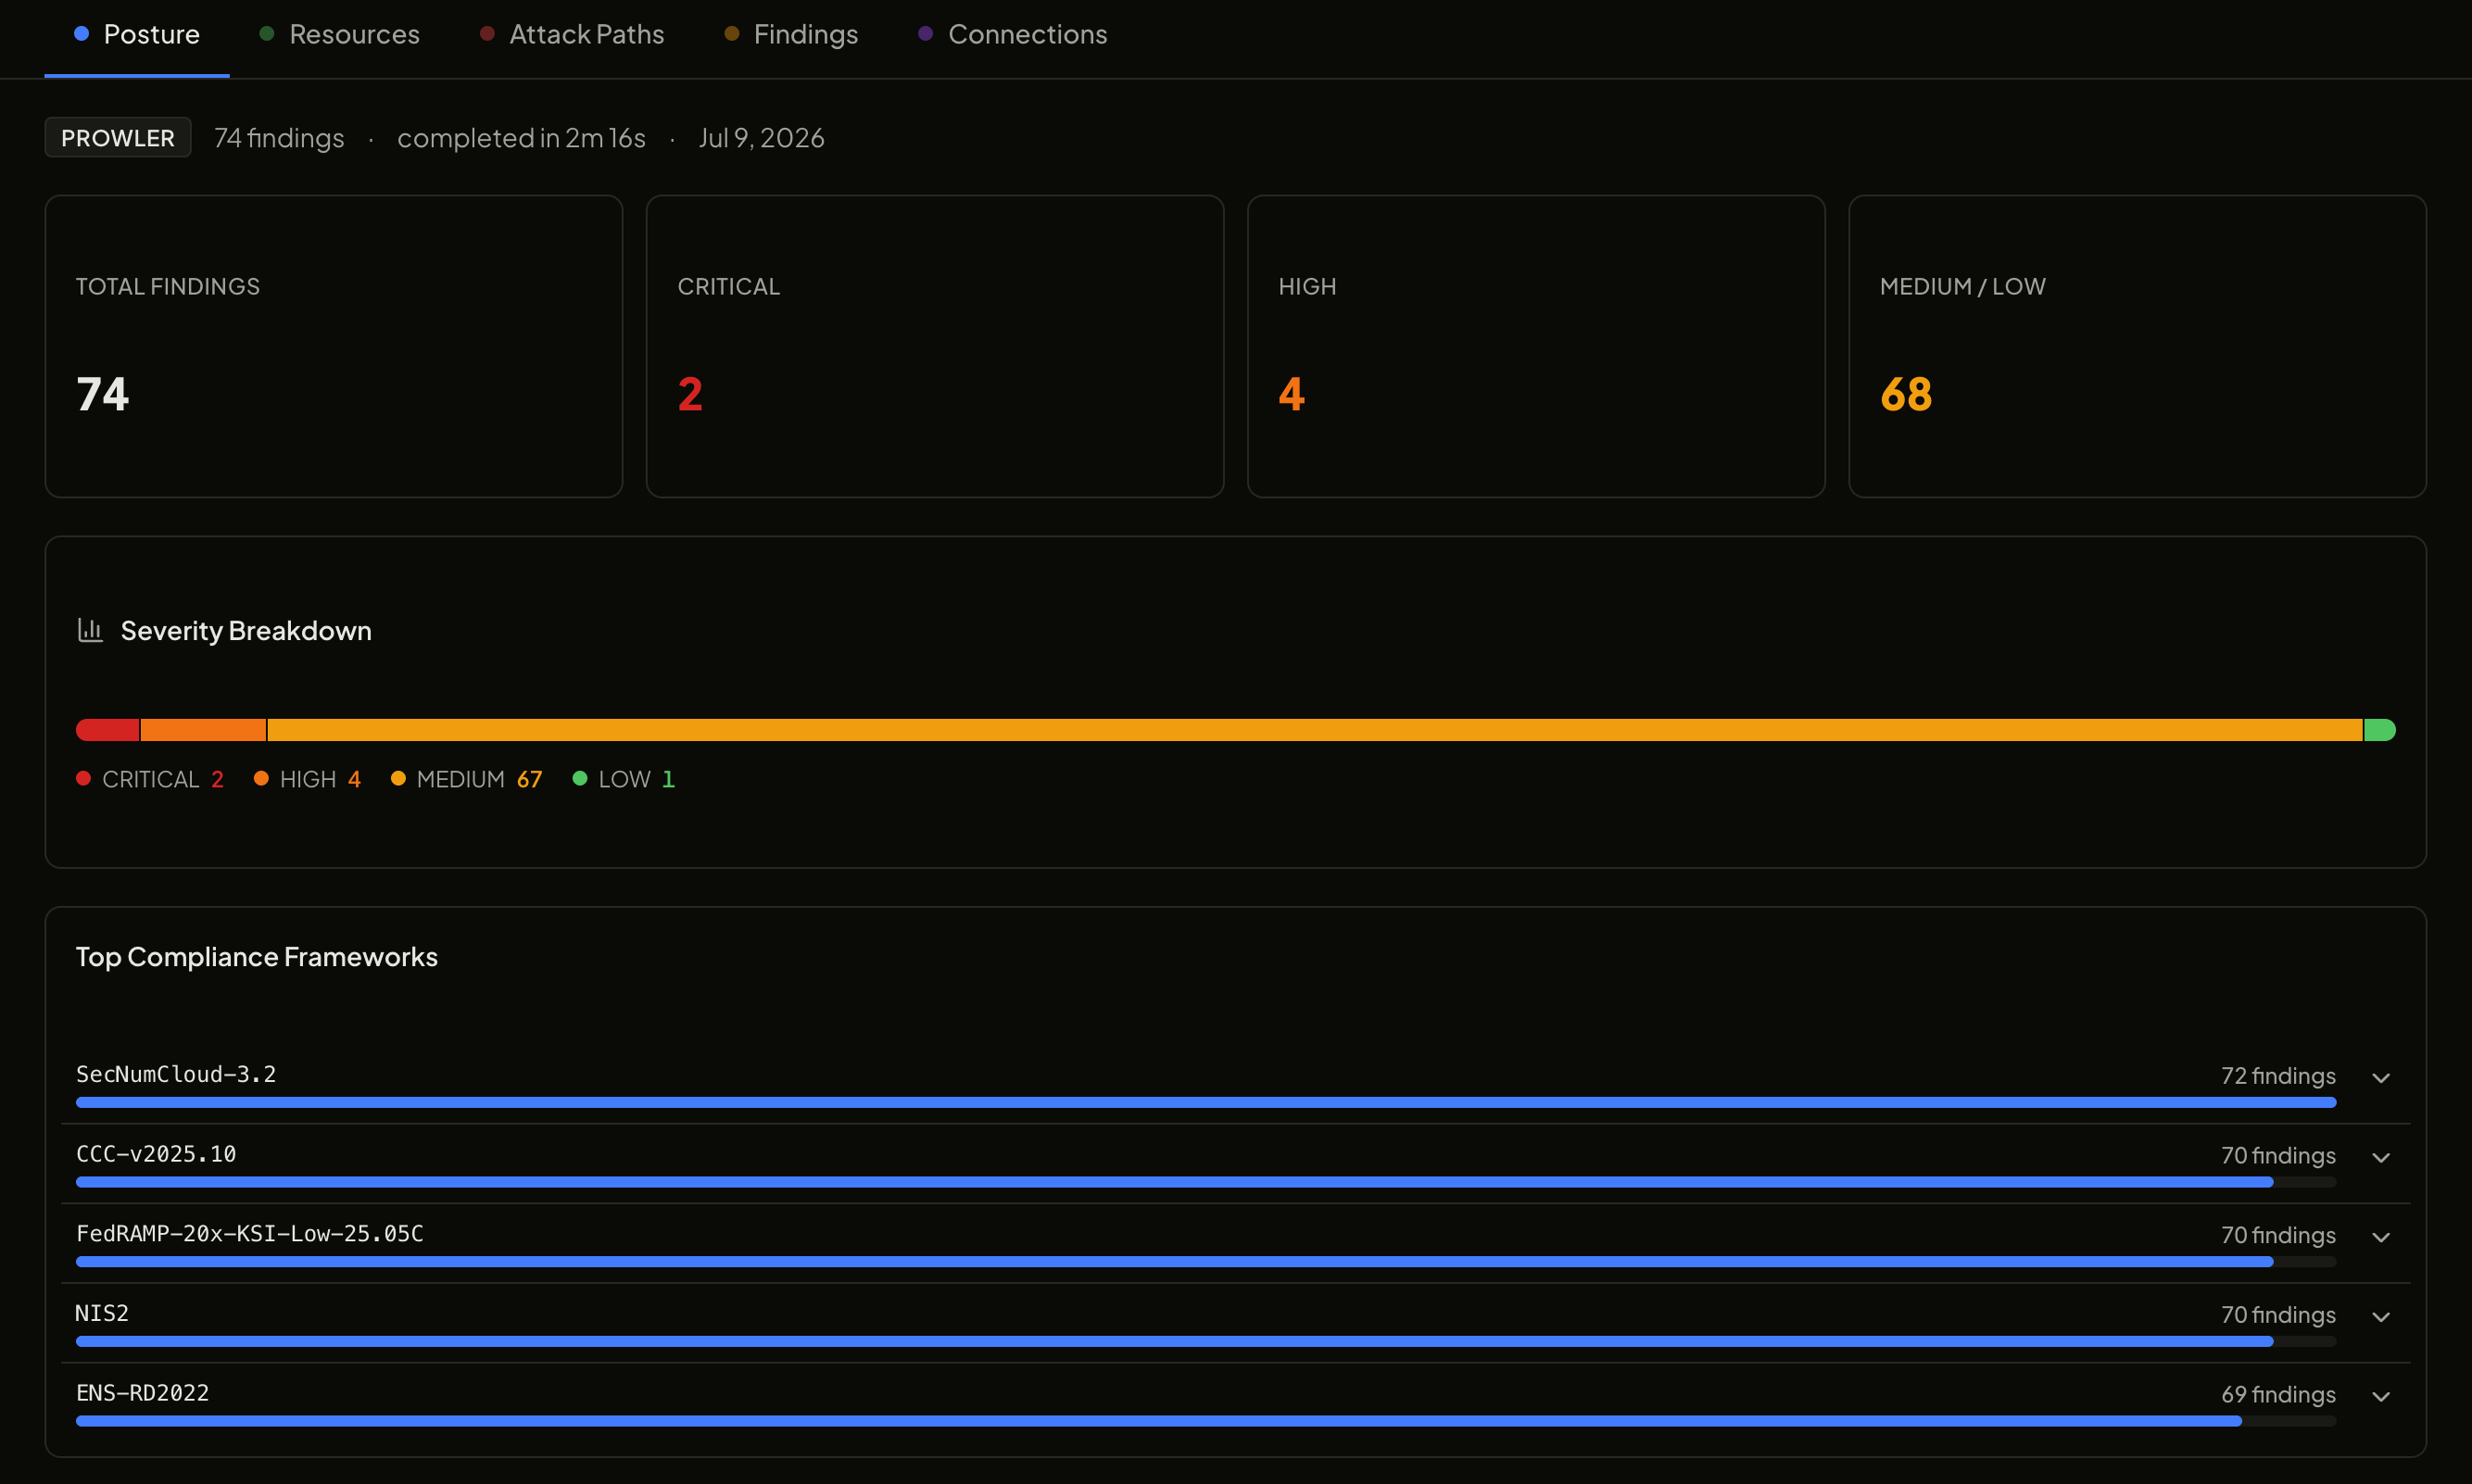
Compliance scores per cloud account for each framework: CIS, ISO 27001, SOC 2, NIST, PCI DSS, DORA and NIS2. Each score shows pass/fail counts and the affected resources, so auditors get evidence, not a summary.
A searchable inventory of every live cloud resource (EC2, S3, RDS, Lambda, VMs, storage accounts, GCE, GKE nodes), each with its findings, IaC origin, permissions and recent runtime events.
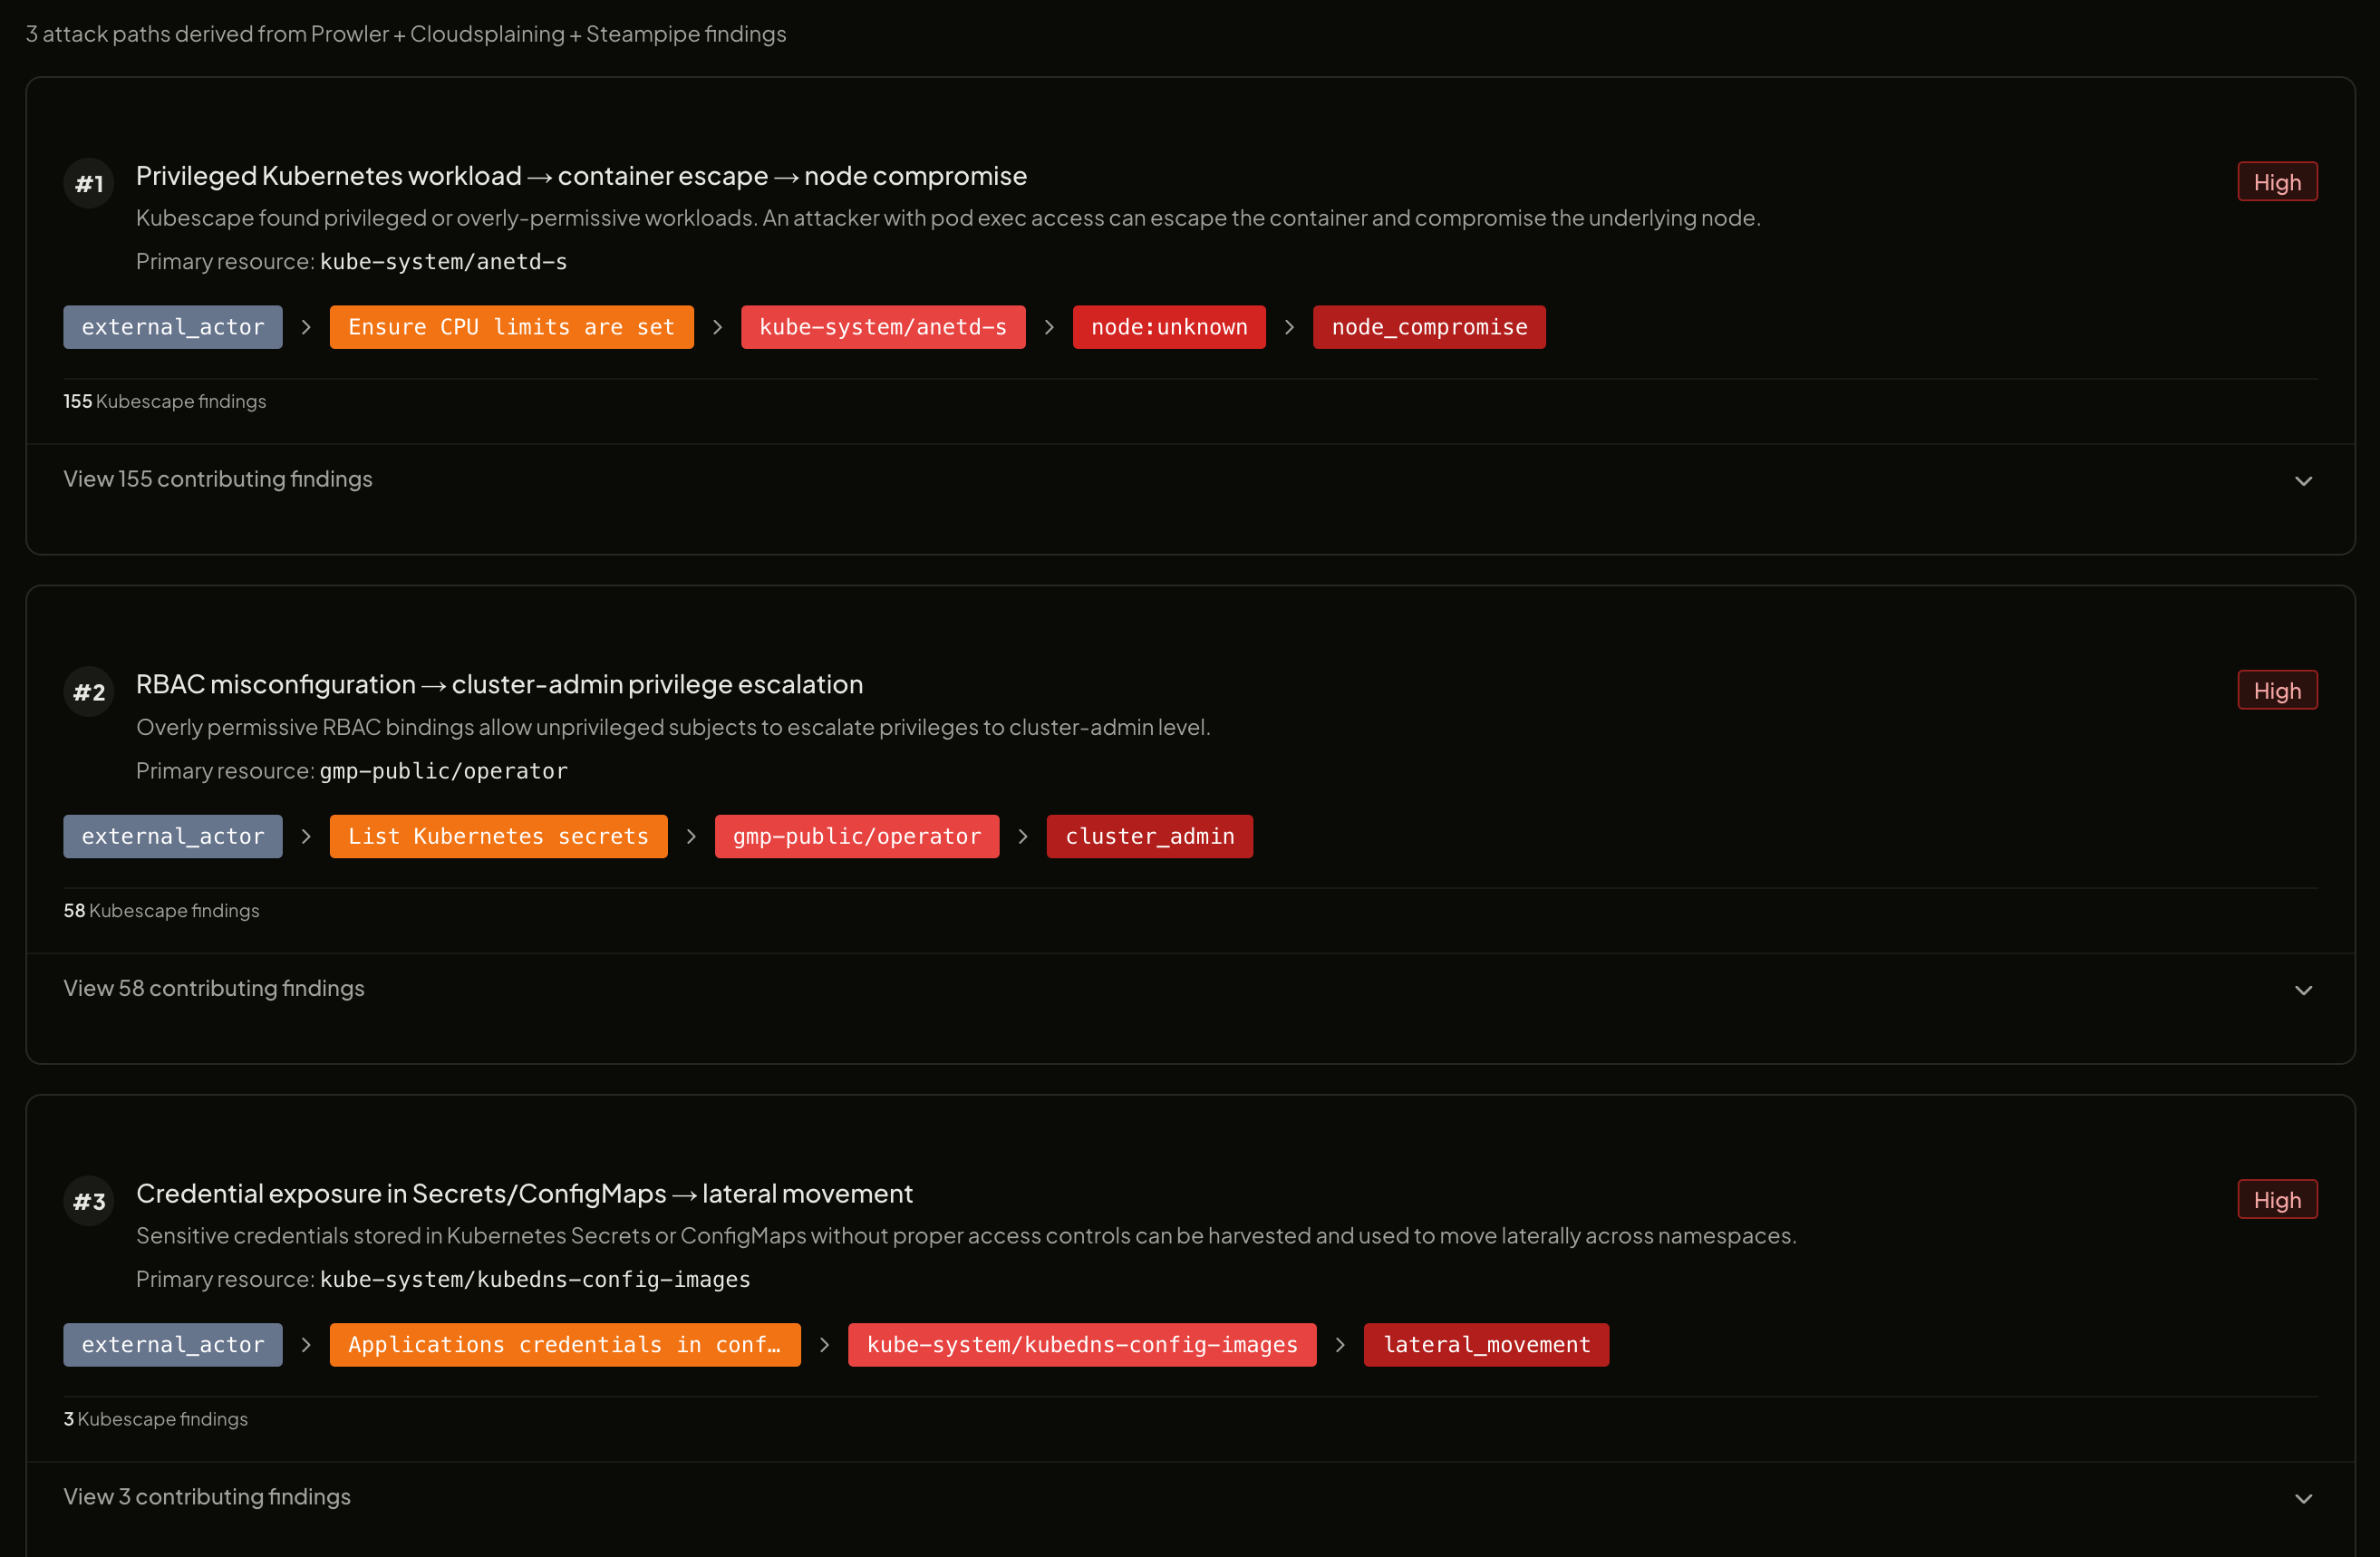
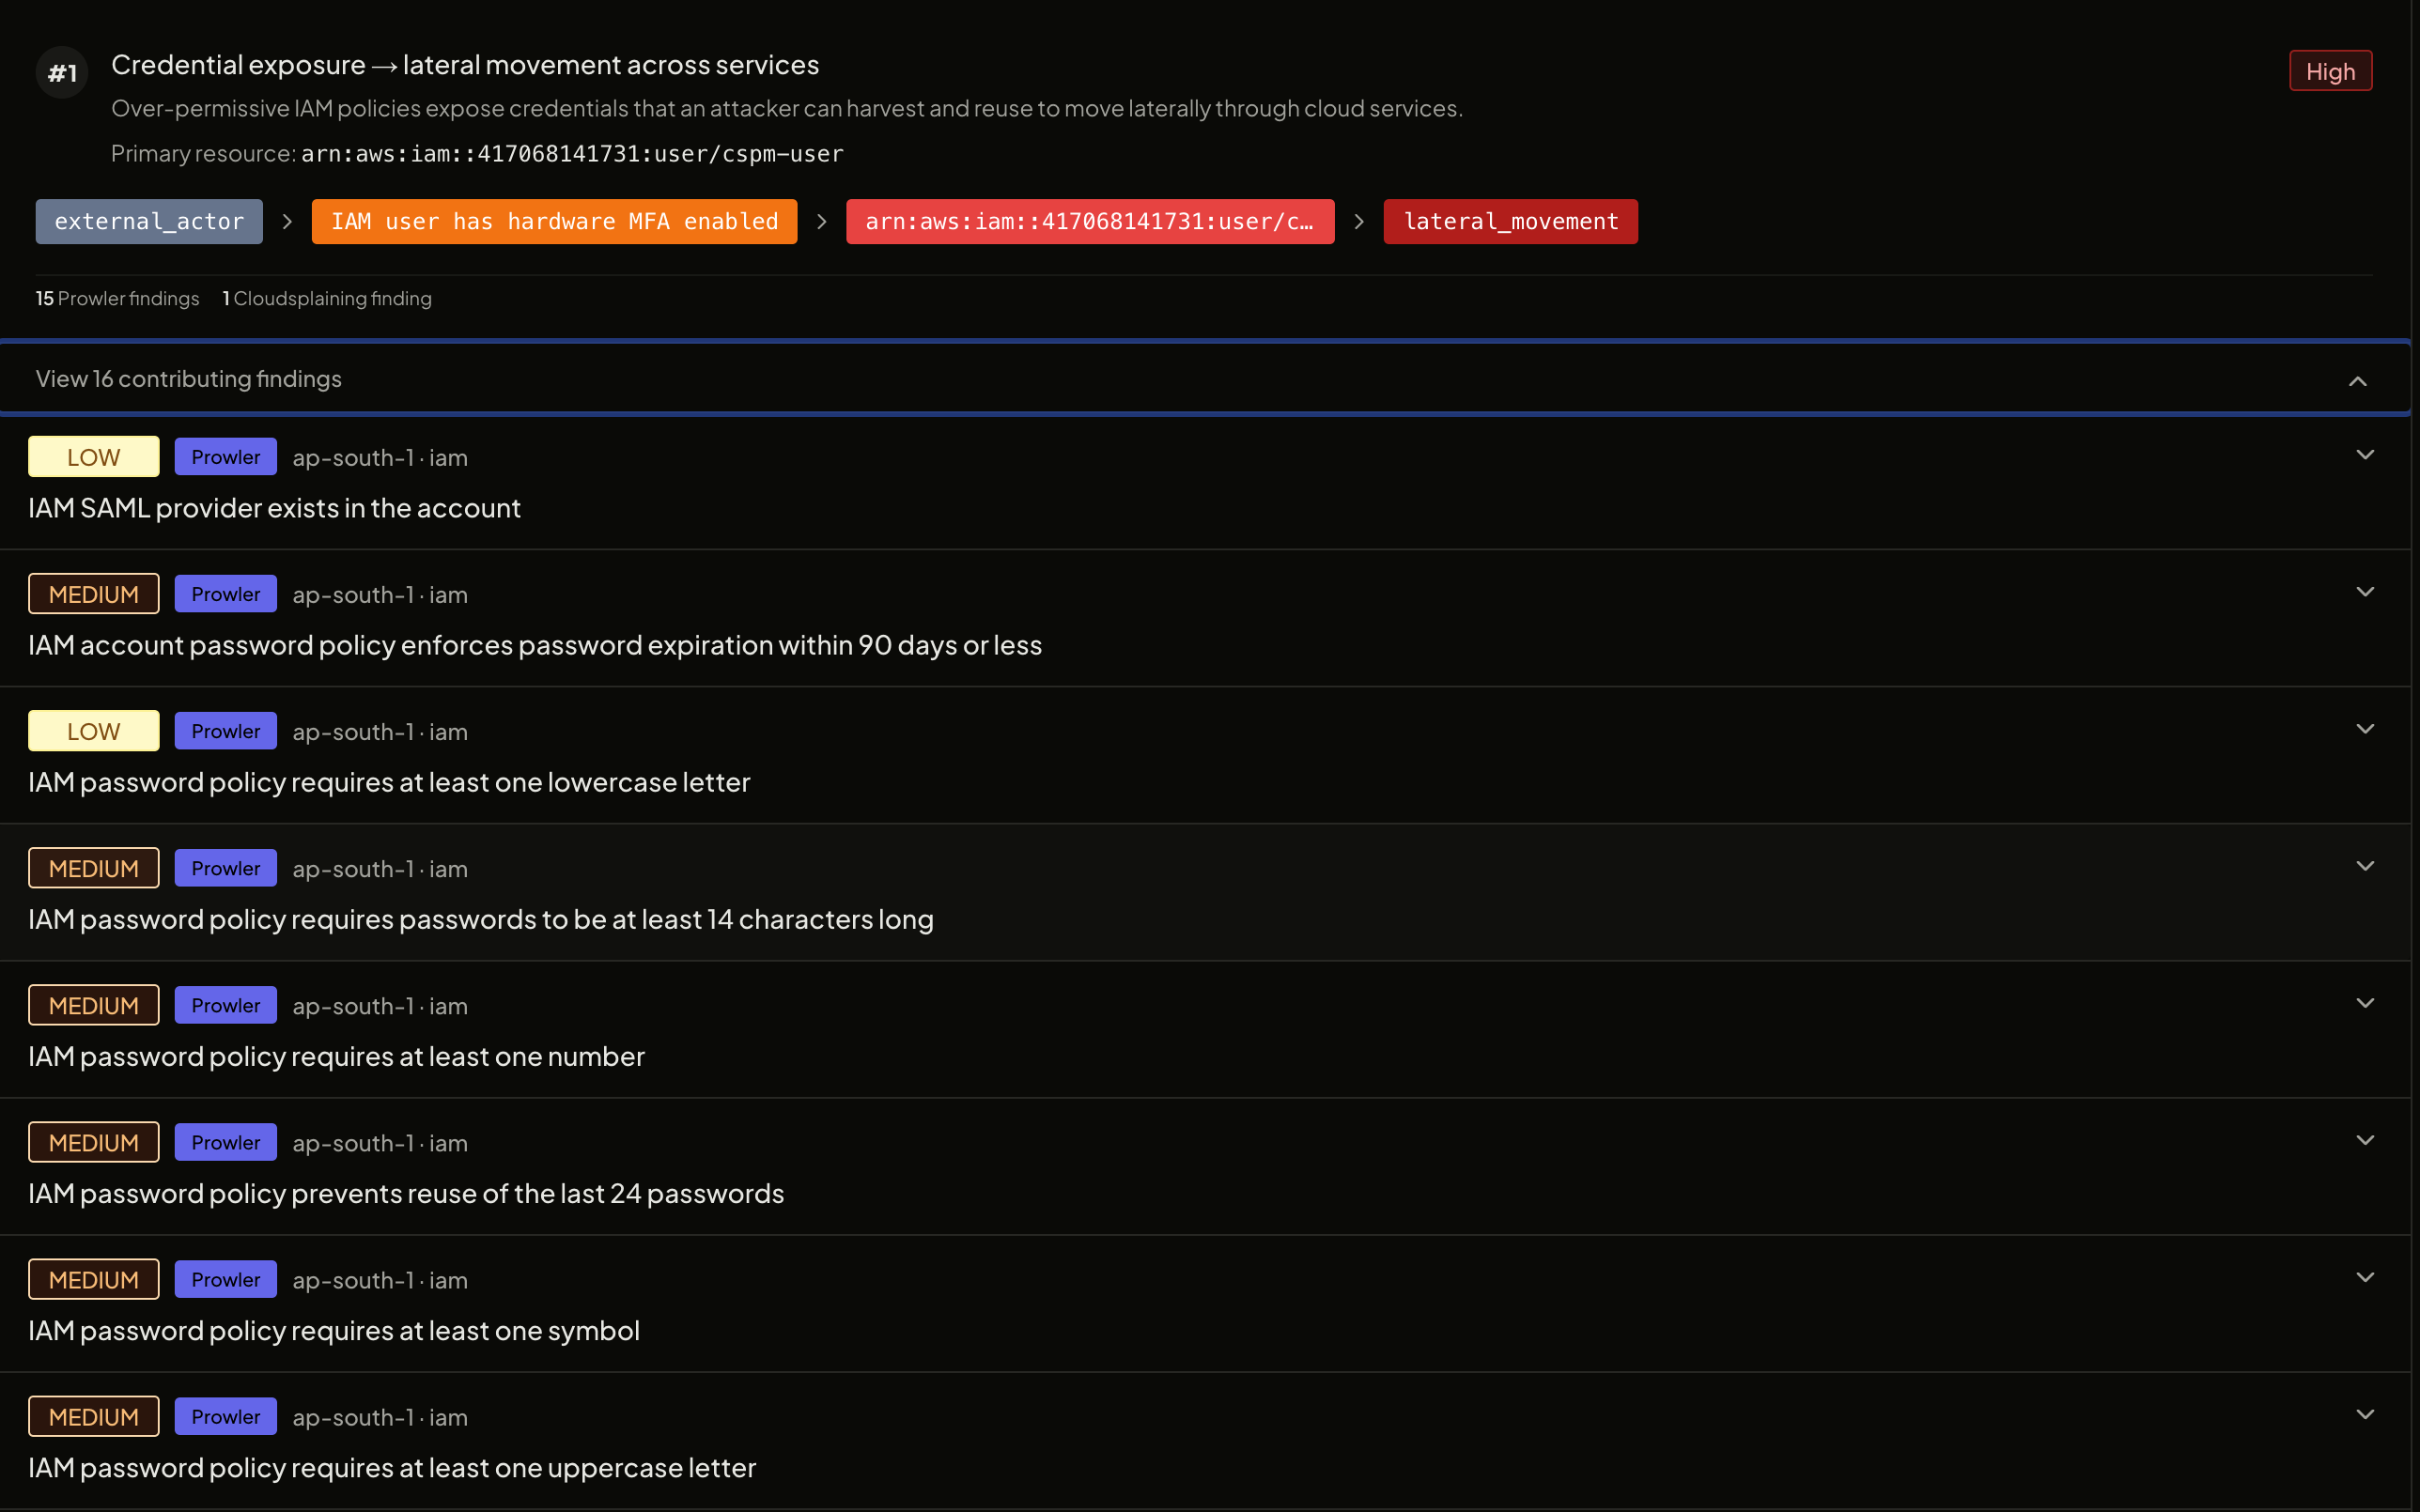
A visual graph of exploitable chains, from first foothold through privilege escalation to sensitive data. Each path is ranked by impact, so your team fixes the chains that matter instead of chasing single findings.
A live Falco eBPF event stream you can filter by severity, namespace, cloud account and event type. Every alert links to its resource, its pre-deployment findings and its IAM context, so investigating takes seconds.
Real scans, real findings, real attack chains. Not mock-ups.
CSPM checks every cloud resource against nine compliance frameworks at once. When the auditor asks for evidence, you export it. Because code findings use the same framework engine, you get one compliance report for your whole stack.
CSPM covers configuration auditing, asset inventory, drift detection, identity analysis and runtime monitoring, across every major cloud provider and Kubernetes.
Auto-remediation is off by default. When you turn it on, an administrator picks which finding types qualify and what action to take. Every action is logged with the resource, account, time, triggering finding and applied fix, and exported to your SIEM.
Prowler, Steampipe, Falco, or Kubescape surfaces a misconfiguration, drift, or runtime threat in your cloud account.
AI filters false positives, deduplicates cross-engine overlaps, enriches with business context, and ranks the finding against your risk threshold.
Cloud Custodian checks the finding against your action policy: alert only, auto-tag, delayed fix or immediate fix.
Action executes using the scoped remediation role. Full context logged to dashboard and SIEM. Notification sent to Slack/Teams/email.
Each cloud connection takes about 5 minutes. AquilaX provides CloudFormation stacks, Terraform modules and Helm charts, so you never manage the scanning tools yourself. Everything is bundled and versioned in the platform.
Cloud provider security centres are a good start, but they don't give the full picture. CSPM adds cross-cloud correlation, IaC drift detection, AI-ranked findings and the link from cloud resource back to code that native tools can't provide.
| Native Cloud Security Centres | AquilaX CSPM | |
|---|---|---|
| Cloud Coverage | Single provider — no cross-cloud view | AWS + Azure + GCP + K8s, unified dashboard |
| IaC Drift Detection | No awareness of IaC source or intent | Field-level diff between live state and Terraform |
| False Positive Rate | Thousands of raw findings, manual triage needed | 10–50 findings per account after Securitron AI |
| Code-to-Cloud Linkage | None — cloud findings are disconnected from code | Every finding traces back to IaC module and code commit |
| IAM Analysis | Basic access advisor, no escalation paths | Full privilege escalation graphs via Cloudsplaining |
| Runtime Detection | Partial — CloudTrail events only, no kernel-level | eBPF kernel events + cloud audit logs via Falco |
| Compliance Reporting | Single framework, no cross-cloud audit export | 9 frameworks, unified PDF + per-control evidence |
| Attack Path Analysis | Individual findings, no chain visualisation | Ranked attack graphs with impact scoring |
| AppSec Integration | Separate tool from code scanners | Same platform as SAST, SCA, IaC, Container scanning |
| Auto-Remediation | Limited, proprietary, AWS-only | Multi-cloud, fully audited via Cloud Custodian |
Cloud security programmes stall when a team faces thousands of unranked findings. CSPM with Securitron AI means fewer findings, faster fixes and compliance that stays current.
Connect your first cloud account in 5 minutes and get the first scan in under 15. Nothing to install on your workloads: just a read-only role, plus a Helm chart if you want runtime detection.